NINE TRIANGLES BAGS DIGITAL STRATEGY MANDATE FROM EUDAEMON
12 Feb, 2024


Most businesses do not think too much about the technology that runs their website. As long as the website is working, pages are loading and enquiries are coming in, there is usually little reason to look under the hood.
But there is a difference between a website that is working and a website that is secure.
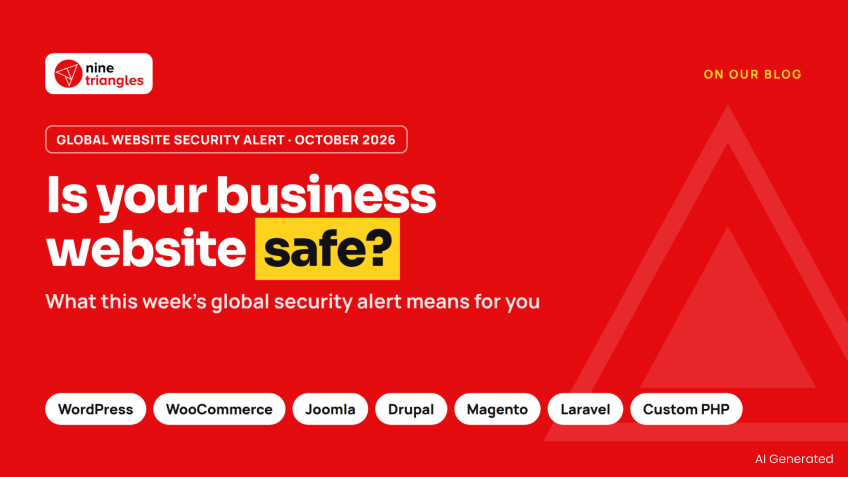
On 21 October 2026, the PHP team released emergency security updates to address two critical vulnerabilities in PHP. Identified as CVE-2026-109618 and CVE-2026-109619, these vulnerabilities could allow an attacker to execute code on a vulnerable server without logging in.
The concern is that an attacker may be able to run unauthorised code on the server and potentially access sensitive information. This is not just a concern for websites that are already showing problems. A website can continue to work normally even when its underlying technology has a security issue.
If your website runs on WordPress, WooCommerce, Joomla, Drupal, Magento, Laravel, OpenCart or custom PHP, this is something worth checking immediately.
The important question is not simply whether your website is working today. It is whether the PHP version running behind it has been patched, and whether there are any signs that someone has already tried to exploit it.
The vulnerability is not limited to one content management system or website platform. The underlying PHP runtime is the concern.
This means websites built using the following platforms should be checked:
- WordPress: Corporate websites, blogs, landing pages and other sites built on WordPress.
- WooCommerce: Online stores running on WordPress.
- Joomla and Drupal: Websites using these PHP-based content management systems.
- Magento and OpenCart: eCommerce websites running on PHP.
- Laravel: Custom web applications and business platforms built using the Laravel framework.
Custom PHP websites: Applications developed specifically for a business, including older websites that may not have been updated for some time.
The same concern applies to other applications and services that use an affected PHP runtime, even if they do not appear to be conventional websites.
Updating WordPress, installing a security plugin or changing your website password does not, by itself, fix a vulnerability in PHP.
The PHP version running on the server needs to be checked and the appropriate security update applied.
This is the first practical step, and it does not require you to understand the underlying code.
If your website runs on WordPress
Log in to the WordPress administration panel and navigate to:
Tools → Site Health → Info → Server
Look for the PHP version information.
The exact menu or information displayed may vary slightly depending on your WordPress version and hosting setup.
If your website is hosted elsewhere
Log in to your hosting control panel and look for the PHP configuration or PHP version settings. The location will depend on the hosting provider.
If you do not have access to these settings, ask your hosting provider or website developer to confirm the PHP version being used by the live website.
One important point: a server can have more than one PHP version installed. Different websites, subdomains, background jobs or application services may use different versions. Checking one website or one setting does not necessarily establish that every application on the server has been covered.
If your business has multiple websites, microsites or landing pages, each of them should be accounted for.
There are five practical steps to take.
1. Identify the PHP version
Start with the live website and confirm the actual PHP runtime being used. Do not rely only on the version mentioned in an old development document or hosting invoice.
2. Apply the security update
Update PHP to an appropriate fixed version. If the website is hosted on a managed platform, contact the hosting provider and confirm when the patch will be applied.
Older PHP versions may no longer receive security updates from the main PHP project. Some hosting providers and software vendors provide their own security fixes, while other installations may need to be upgraded to a supported version.
Ask your developer or hosting provider to confirm the appropriate fix for your specific environment.
3. Test before and after the upgrade
An older website may depend on functions or libraries that behave differently in a newer PHP version. Test the upgrade on a staging copy wherever possible, then verify the live website after deployment.
Check important functions such as login, forms, payments, database operations, integrations and any business-critical workflows.
The aim is to fix the vulnerability without introducing another problem.
4. Check for signs of compromise
Patching is essential, but it does not tell you whether someone has already exploited the vulnerability.
Review server and application logs for unusual activity. Look for unexpected files, unfamiliar administrator accounts, suspicious changes to website code and unexplained errors or processes.
These are indicators to investigate, not proof of an attack on their own. If you find anything suspicious, involve a qualified security professional to investigate the incident and determine the appropriate response.
5. Review the wider security setup
A patched PHP runtime addresses these particular vulnerabilities. It does not automatically make the entire website secure.
Check that the CMS, plugins, themes, libraries and server software are also maintained. Review access permissions, backups, monitoring and firewall configuration.
A web application firewall can provide an additional layer of protection, but it should not be treated as a replacement for applying the required security updates.
This is a fairly common situation.
A website may have been built several years ago, and upgrading PHP could affect its design, plugins, integrations or other functionality. In some cases, the original developer may no longer be available.
Ignoring the vulnerability is not the answer.
Start by identifying the version in use and speaking to the hosting provider or a developer who can assess the application. Depending on the environment, a supported security fix may be available. Otherwise, the website may need to be migrated to a supported PHP release.
If immediate patching is not possible, assess the exposure and follow the relevant official security guidance. Where an internet-facing application cannot be remediated promptly, temporarily isolating it from public access may need to be considered.
The important thing is to have a clear remediation plan and not leave the website running indefinitely on an unsupported version without understanding the risk.
It may be, depending on the PHP version and runtime configuration used by your hosting environment. Check the PHP version and confirm that the applicable security fix has been installed.
Not by itself. WordPress updates and PHP runtime updates are separate. Your hosting environment needs to run a PHP version containing the relevant security fixes.
Older PHP versions may no longer receive security updates from the main PHP project. Some vendors provide their own security fixes, so the correct remediation depends on your hosting environment. Do not assume an older installation is protected without confirmation.
A security plugin may help detect suspicious activity or protect against certain attacks. However, it does not replace patching the underlying PHP runtime. Additional protections should be used alongside the appropriate update.
You cannot establish this simply by checking whether the website is loading normally. A security review should include relevant logs, files, accounts and other indicators of compromise. If an attack is suspected, patching should be accompanied by an investigation.
It depends on how your website is hosted. A managed hosting provider may control the runtime, while a developer or internal IT team may manage it on a VPS or dedicated server. The important thing is to confirm who owns the task and verify that the update has actually been applied.
At Nine Triangles, our Technology Lab works with websites, web applications and digital platforms across different technology stacks.
If you are unsure which PHP version your website is running, whether the appropriate security update has been applied, or whether an older website needs a more detailed review, we can help.
We can check the PHP environment, assess the website's exposure, help plan the required patch or upgrade, and review potential signs of compromise.
The first step is simple: identify what your website is running and establish whether it has been fixed.
If you manage a business website, or know someone who does, share this advisory with them. It is worth checking now rather than waiting for a problem to appear.
Canadian Centre for Cyber Security:
European Union Agency for Cybersecurity (ENISA):
This article provides general security guidance based on information available on 22 October 2026. The appropriate remediation depends on the PHP version, hosting environment and application configuration. A website-specific assessment is needed to establish its actual exposure.
With strategy and insights at the core, we seamlessly integrate creative, technology, video, SEO, and performance marketing to deliver projects on time and within budget. That's why clients of all sizes and industries trust us for their most diverse and dynamic needs.



We combine the agility of a mid-sized agency with the strategic depth of a consulting partner. Every project starts with a business lens - focused on outcomes, not just outputs.
In short, we are not just a digital agency. We are your digital growth partner.
We are all three - by design.
Our model is built to support modern business needs through integrated services across strategy, design, technology, and performance marketing. We help you define the problem, build the solution, and scale the impact.
We complement, not compete.
Think of us as your extended team - brought in for specific expertise, overflow capacity, or to scale faster. Whether it is UX strategy, campaign content, full-stack development, or performance marketing, we plug in where it matters most.
We work across markets and time zones.
Our teams are based in India, but we have delivered for clients in the Middle East, Europe, the US, Southeast Asia, and beyond. We adapt our workflows to suit your region, your rhythm, and your goals.
Simple - just reach out.
We will begin with a conversation to understand your needs and identify how we can support you. From there, we tailor the right approach - whether it is a quick sprint or a long-term roadmap.
© 2026 All Rights Reserved